

Manage all your network devices in one place.
Retivo backs up the configs of your switches, routers and firewalls, shows you every change line by line, tells you which devices need patching, and keeps the evidence ready for your next audit. It runs inside your network. You work from anywhere.
Free for personal use, no card needed.
- core-sw-01Cisco IOS XENo change
- dist-sw-02Aruba CXNo change
- edge-fw-01FortiGate2 lines changed
- br-rtr-07MikroTikNo change
- ap-ctrl-01Aruba Instant On1 critical CVE
config firewall policy
    edit 12
-       set srcaddr "all"
+       set srcaddr "office-lan"
-       set service "ALL"
+       set service "HTTPS" "SSH"
nextWorks with


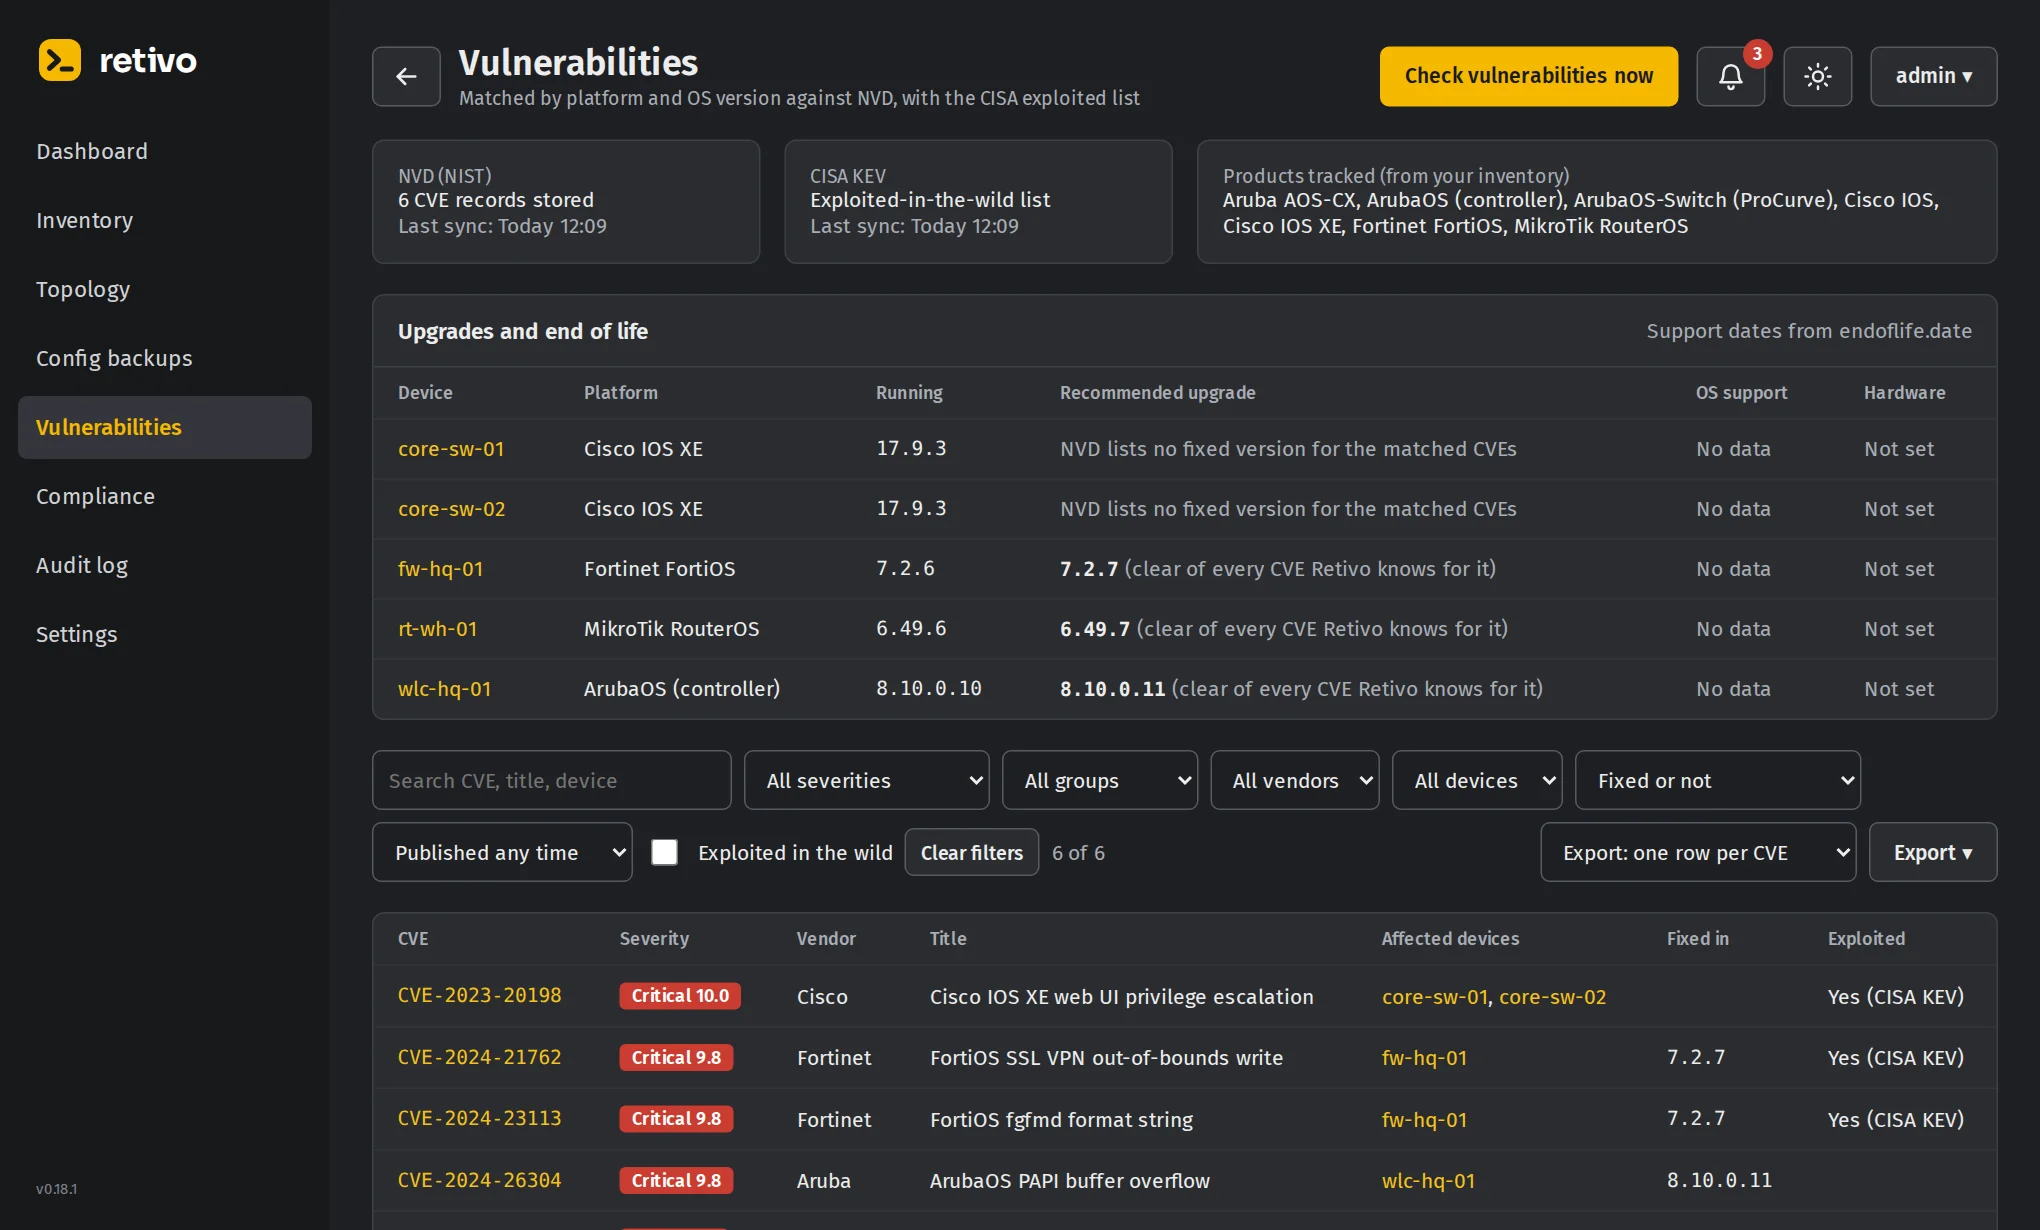
Know which devices are vulnerable before an attacker does.
Every night Retivo reads the exact OS version running on each device and checks it against the NIST National Vulnerability Database and CISA's list of vulnerabilities exploited in the wild. You see what affects you, how bad it is, and which version fixes it.
- Exact versions read over SNMP or SSH, not guessed from a model name
- Exploited in the wild flagged first, straight from the CISA catalog
- The fix: the version that closes every known CVE, and when support ends
Everything a network team checks, in one place.
Built by a network engineer for the jobs you do every week, not for a slide deck.
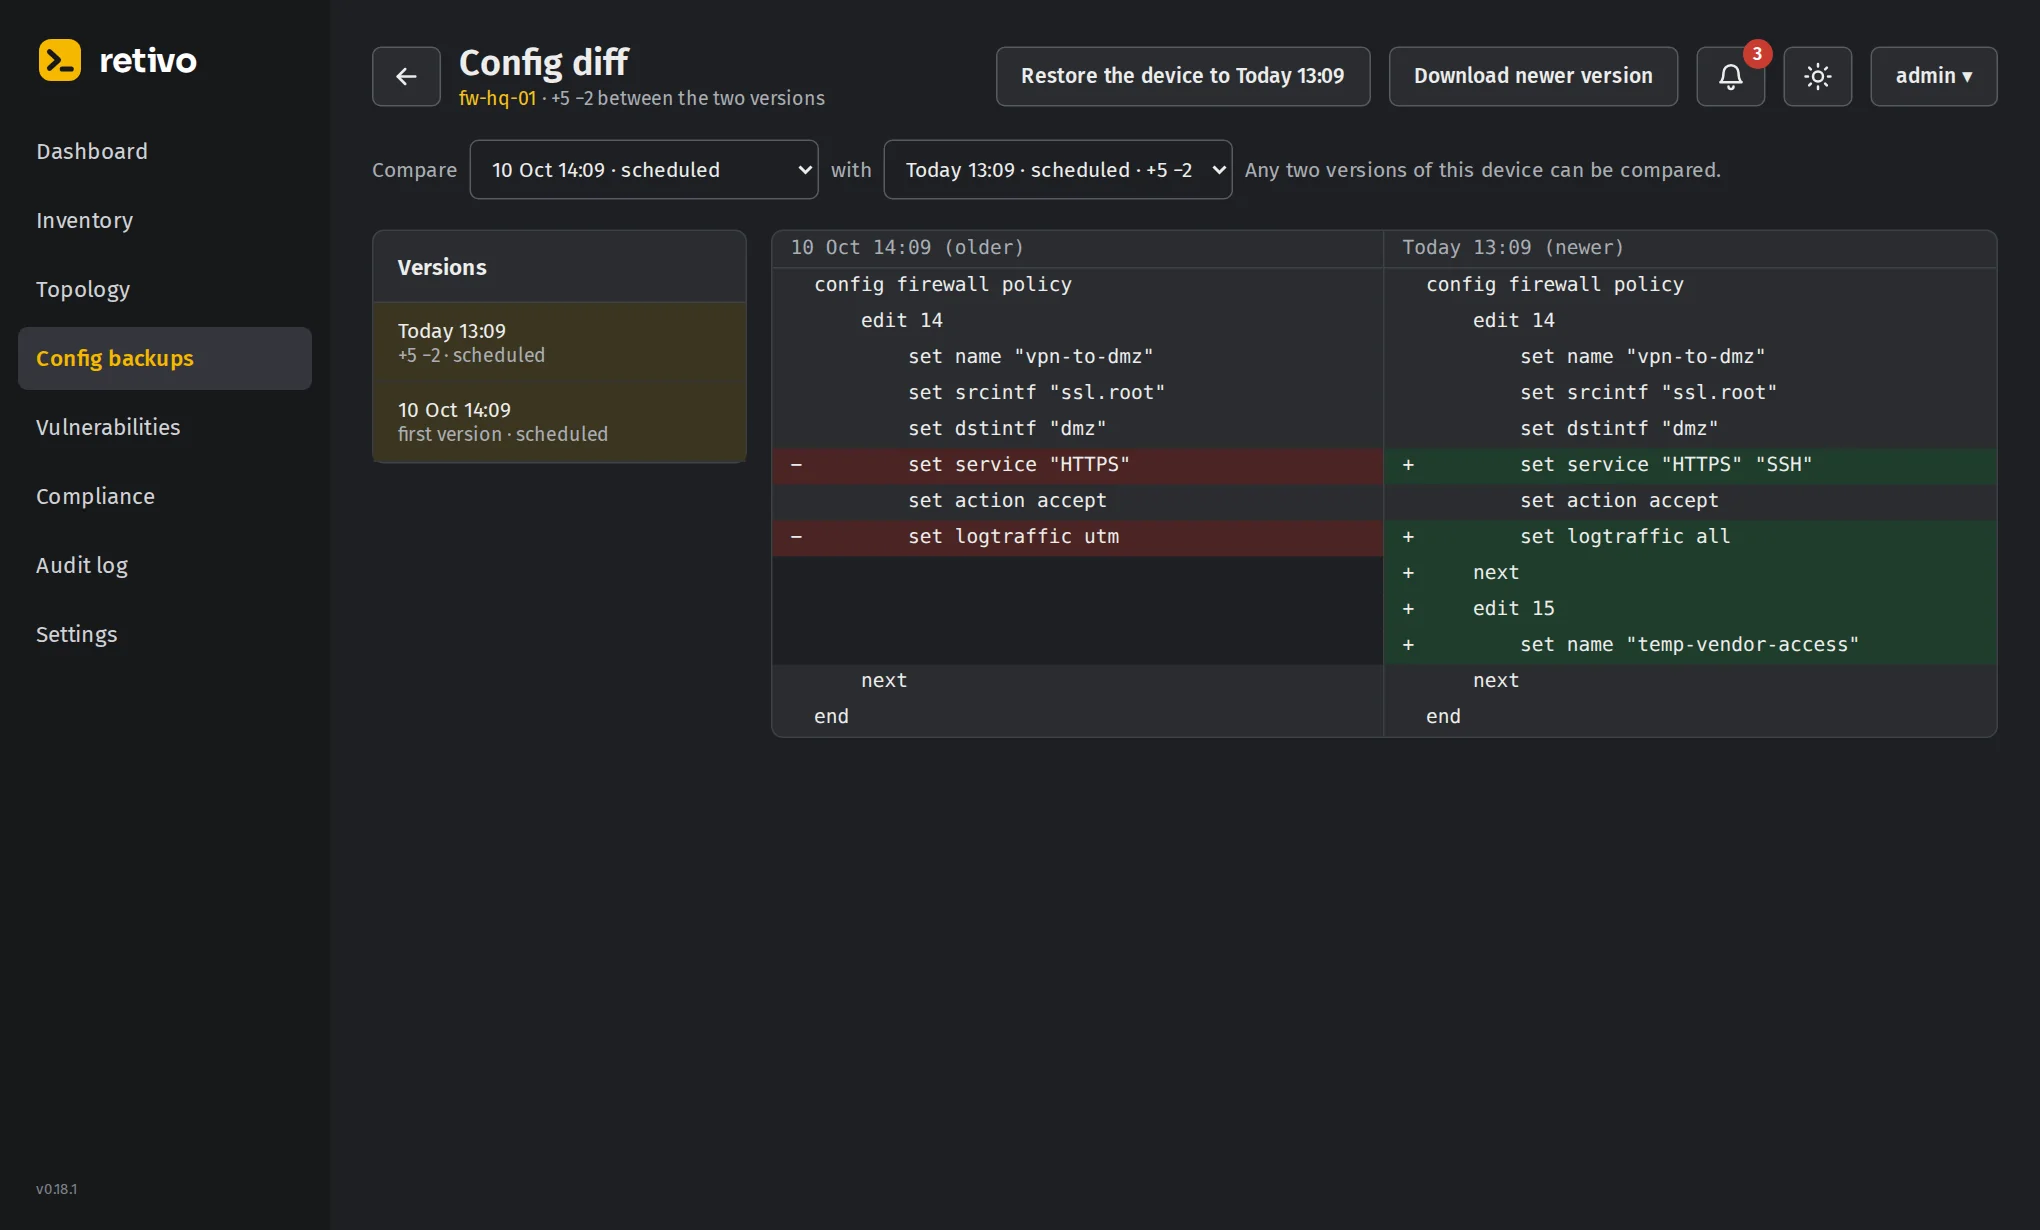
Backups that show you what changed
Every device is backed up daily and whenever you ask. A new version is kept only when the config really changed, and you can compare any two versions side by side. Copies can also go to S3, Google Drive, OneDrive, SFTP, FTP or TFTP.
- Push changes safely
- Send config lines to one device or a hundred. Retivo reads the live config first, shows what will be sent, waits for you to type yes, then shows the real before and after.
- Restore in minutes
- Pick an older version and Retivo proposes the commands that bring the device back to it.
- Compliance rules
- Decide per group whether Telnet, SSH, HTTP and HTTPS must be on or off, and write your own rules that a config must or must not contain.
- Live topology
- A map drawn from LLDP and CDP neighbours, with links that disappeared shown in red. Export it to PDF for the next audit.
- Firmware upgrades
- Upgrade Cisco, MikroTik and FortiGate from the browser, with flash and version checks before anything reboots.
- NetBot
- Ask what is down, what to patch first or how a feature works. Anything it changes waits for your confirmation.
- Roles and audit log
- Give each person only the groups and actions they need. Every action is logged and exports to Excel or PDF.
- Reports
- A weekly or monthly status report by email: devices down, failed backups, changes, vulnerabilities and end of life.
Be ready for every network audit.
Auditors working to ISO 27001, PCI DSS, NIS2 or your own policy ask for the same evidence. Retivo keeps it current, so the answer is an export, not a week of collecting.
Who changed what, and when
Every sign-in, push, restore and setting change is logged with the person and time.
Excel, PDF, CSVConfiguration history
Every version of every device config is kept. Show what a device looked like on any day, compare two versions, restore one.
Text, diffHardening checks
Rules per group: Telnet and HTTP off, SSH and HTTPS on, and lines that must be there, like NTP, syslog and AAA.
Compliance viewPatch status
Each device matched against NVD and the CISA exploited list, with severity and the version that fixes it.
Excel, PDFLifecycle
End of support dates for the OS and hardware you run, so replacements are planned before they are findings.
ReportAsset inventory
Every device with model, serial, OS version, group and location. Pick the columns you need.
ExcelNetwork diagram
A current map built from LLDP and CDP neighbours, not a drawing from three years ago.
PDFAccess control
Roles limited to groups and actions, an email code at every sign-in, or sign-in through Entra ID or Active Directory.
Audit log
Built for teams that run many network devices.
From a single office to hundreds of branches across the UAE and the Gulf, Retivo fits any organization whose switches, routers and firewalls have to be backed up, patched and ready for an auditor.
Managed service providers
A separate company per customer, one view across all of them, and a node at each client site with no VPN to maintain.
MSPs, system integratorsBanks, insurers and fintech
Config history, change log and patch status ready for PCI DSS and central bank inspections, with branch networks backed up every night.
PCI DSS, ISO 27001Government and semi-government
Data stays inside your network, and hardening checks and evidence line up with national information assurance requirements.
UAE IA, DESC ISRHospitals and healthcare groups
Know which clinic firewall needs patching and prove every change to medical-grade networks before the regulator asks.
ADHICS, ISO 27001Energy, utilities and oil and gas
Remote plants and substations with mixed vendors, tracked from one place over an outbound-only connection.
Remote sites, NIS2Hotels, retail and malls
Dozens of properties or stores, each with its own FortiGate or MikroTik, kept consistent and backed up without a site visit.
Multi-site chainsTelecom, ISPs and data centres
Large fleets of routers and switches, bulk pushes with a diff before every change, and firmware upgrades at scale.
Carrier and DC networksSchools and universities
Campus networks run by small IT teams, with a weekly report on what went down, what changed and what needs an update.
Campus IT
Your network data stays in your network.
You install a small Retivo Node next to your devices. It connects out to Retivo, so you never open a port or set up a VPN.
Install the node
Run Retivo Node with Docker on any small Linux server or VM that can reach your devices.
It dials out
The node opens one encrypted outbound connection to dash.retivo.net. No inbound rules, no port forwarding, no VPN.
Work from anywhere
Sign in at dash.retivo.net. Your requests travel through that connection to your node and back.
Stays on your node
- Device passwords, SSH logins and SNMP communities
- Every config version and backup
- Inventory, topology, audit log and the database itself
Kept by Retivo
- Your organization and its users
- Which nodes belong to you, and whether they are online
- Your plan and licence
Pages you open pass through the relay encrypted and are never stored there.
Free for personal use. Enterprise for business.
No feature tiers. Vulnerability checks, compliance, firmware upgrades and NetBot are in both plans.
Enterprise
Custom
quoted for your network
- Every feature, for commercial use
- As many devices, nodes and users as you need
- A company per customer for MSPs
- Priority email and phone support
- Invoice and bank transfer
Questions
Does Retivo see my device passwords?
No. Credentials, configs and the database live on the Retivo Node in your network. The cloud keeps your organization, users and licence, and relays the pages you open without storing them.
What do I need to run the node?
A Linux server or VM with Docker that can reach your devices over SSH or SNMP, and outbound HTTPS to the internet.
What happens if the internet connection drops?
The node keeps backing up, checking and logging on its own. You see everything again as soon as it reconnects.
Will Retivo help with our audit?
Yes. It keeps the usual evidence current: config history, change log, hardening checks, patch status, end of life dates, inventory and a network diagram, each exportable to Excel or PDF. It does not certify you; it gives your auditor the facts quickly.
Which vendors are supported?
Cisco IOS and IOS XE, Fortinet FortiGate, MikroTik RouterOS, Aruba (AOS-S, CX and Instant On), Juniper, Huawei, TP-Link, Ubiquiti and Starlink, with more added regularly.
Can I count devices by group or client?
Yes. Each organization sees its own device count and plan, and MSPs see all their clients together.